


Guardrails
Deploy pre-call and post-call guardrails in nRouter to prevent prompt injections, enforce content safety policies, and redact sensitive PII data in real time.
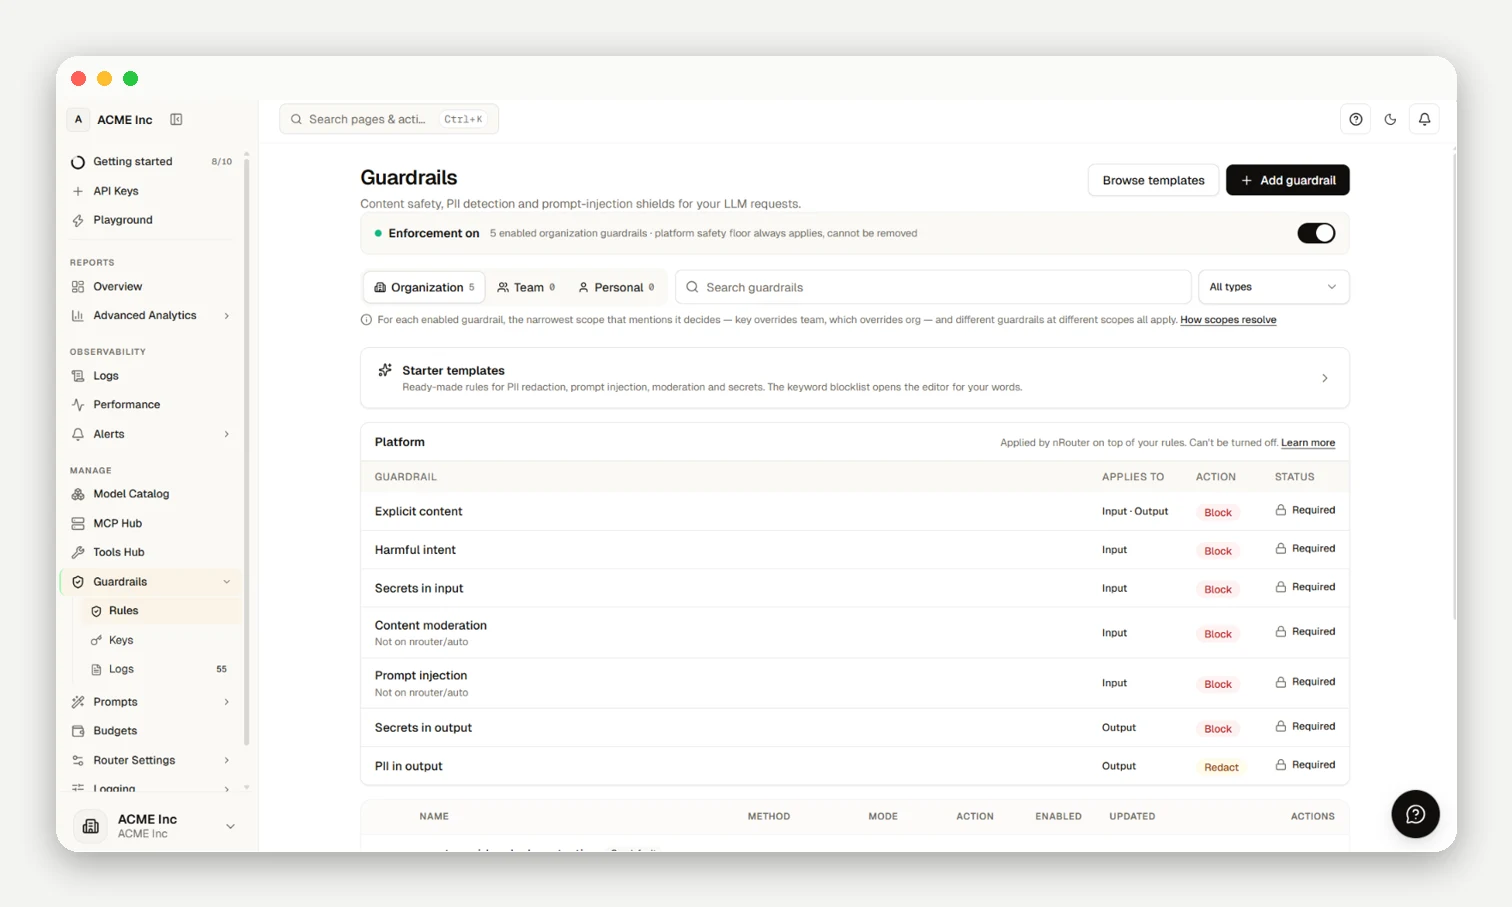
nRouter guardrails enforce real-time input sanitization, PII redaction, credential leak protection, and prompt injection defense before requests hit upstream models (pre-call) and before responses reach clients (post-call). All rules execute transparently within the gateway without application code changes, ensuring comprehensive safety policies and regulatory compliance.
Guardrail Types
| Type | Target | Phases | Actions |
|---|---|---|---|
| PII Scanner | 21 personal identifier types with Luhn and format checks | Pre/Post-call | Block, Redact, Warn, Log |
| Keyword | Exact and case-insensitive word matching (blocked_keywords) | Pre/Post-call | Block, Redact, Warn, Log |
| Prompt Injection | Instruction overrides, persona hijacks, exfiltration beacons | Pre/Post-call | Block, Warn, Log |
| Secret Scanner | API keys, private keys, cloud tokens, database credentials, JWTs | Pre/Post-call | Block, Warn, Log |
| Explicit Content | Sexually explicit content and CSAM with obfuscation unfolding | Pre/Post-call | Block, Warn, Log |
| Content Moderation | Model-scored harassment, hate speech, self-harm, toxicity | Pre-call | Block, Warn, Log |
| Prompt Injection (model-scored) | Model-scored jailbreak classification and adversarial detection | Pre-call | Block, Warn, Log |
Enforcement Actions
| Action | Pre-Call Behavior | Post-Call Behavior |
|---|---|---|
| Block | Rejects with 400 (x-nr-guardrails: blocked) and $0 spend on blocked requests. | Suppresses response; prior compute remains billable. |
| Redact | Replaces sensitive tokens with masks (e.g. [REDACTED_EMAIL]). | Masks buffered text; halts streams to prevent leaks. |
| Warn | Forwards request; records violation in telemetry. | Forwards response intact; logs violation in audit trail. |
| Log | Silent pass-through; records evaluation metadata. | Silent pass-through; records evaluation metadata. |
Scopes & Platform Floor
- Hierarchy:
Virtual Key→Team→Organization. Most specific tier governs. - Gate 0: Evaluates platform holds and revoked keys before holds occur, guaranteeing $0 spend on blocked requests.
- Immutable Floor: Every request blocks explicit content, harmful intent, and secret leak blocking — secrets in prompts and responses (blocked) pre-call and post-call, plus response PII redaction. No override can weaken this floor.
- Threats: Covers direct jailbreaks, indirect injections, exfiltration beacons, and phishing across 9 languages (English, Dutch, French, German, Hindi, Italian, Portuguese, Spanish, Thai). Model timeouts fail closed (
503withx-nr-guardrails: unavailable).
Supported PII Categories
| Domain | Identifiers | Validation Standard |
|---|---|---|
| Contact & Identity | EMAIL_ADDRESS, PHONE_NUMBER, US_SSN, US_PASSPORT, US_DRIVER_LICENSE, NATIONAL_ID, US_ITIN, EMPLOYEE_ID | Format regex and contextual labeled proximity |
| Financial & Banking | CREDIT_CARD, IBAN_CODE, SWIFT_CODE, US_BANK_NUMBER, ABA_ROUTING_NUMBER | Luhn checksum and ISO-13616 standards |
| Network & Device | IP_ADDRESS, IPV6_ADDRESS, MAC_ADDRESS, DEVICE_IDENTIFIER, VEHICLE_IDENTIFICATION_NUMBER | Octet and hardware format validation |
| Healthcare & Biometric | MEDICAL_RECORD_NUMBER, HEALTH_PLAN_BENEFICIARY_NUMBER, BIOMETRIC_IDENTIFIER | Contextual identifier patterns |
Per-Request & Telemetry
Pass nrouter_guardrails: ["pii-strict"] in JSON payloads (add-only, max 8 org-owned IDs). Responses report posture in x-nr-guardrails: none, monitor, pass, redacted, partial, blocked (incurs $0 spend), or unavailable. Manage rules and immutable version snapshots under Guardrails in the dashboard (Owner/Org Admin required).
Next Steps
Frequently asked questions
If a guardrail blocks a request, am I still charged credits for it?
Pre-call blocks cost nothing ($0 spend); post-call blocks withhold the response but upstream tokens already generated remain billable.
Can a request turn a guardrail off for one call?
No, nrouter_guardrails is strictly add-only and can never remove or weaken configured rules or the platform safety floor.
What happens if I name a guardrail that doesn't exist?
The request returns 400 guardrail_not_found, byte-identical whether the ID is nonexistent or belongs to another organization.
Who on my team can create or edit guardrails?
Creating, editing, deleting, and rolling back rules requires Owner or Org Admin privileges; members have read-only visibility.